The O365 Intrusion-TryHackMe Walkthrough
What is the first timestamp at which a non-macOS device signed into Marcus Webb’s account? (Format: YYYY-MM-DD HH:MM:SS)

Ans: 2026–08–27 12:28:31
Just after logging in, the attacker accessed a large number of emails within the first few minutes of the session. How many emails were accessed during this window?


Ans: 22
What subject line does the attacker’s inbox rule match on?

Ans: invoice
How much time elapsed between the malicious inbox rule being created and a matching reply email arriving in the mailbox? (e.g. 2 minutes 51 seconds)

Rule created: 12:30:10
Matching email arrived: 12:41:09
Calculate:
12:41:09 − 12:30:10 = 10 minutes 59 seconds
Ans: 10 minutes 59 seconds
Marcus Webb’s account logged a Teams message that had a link attached to it. What file did this link reference?

Ans: Meridian_Invoice_Batch_Aug2026.pdf
What operating system was used in the suspicious sign-in to David Chen’s account?
Ans: invoice
How much time elapsed between the malicious inbox rule being created and a matching reply email arriving in the mailbox? (e.g. 2 minutes 51 seconds)
Rule created: 12:30:10
Matching email arrived: 12:41:09
Calculate:
12:41:09 − 12:30:10 = 10 minutes 59 seconds
Ans: 10 minutes 59 seconds
Marcus Webb’s account logged a Teams message that had a link attached to it. What file did this link reference?
Ans: Meridian_Invoice_Batch_Aug2026.pdf
What operating system was used in the suspicious sign-in to David Chen’s account?

Ans: linux
What IP address was used in this same sign-in?
Ans: 91.219.237.88
How much time passed between this message being created and the suspicious sign-in to David Chen’s account? (e.g. 2 minutes 51 seconds)
Message created: 13:03:38
Suspicious sign-in: 13:27:04
Elapsed time: 23 minutes 26 seconds.
Ans: 23 minutes 26 seconds
The file the attacker downloaded from David Chen’s account was legitimately modified earlier that day. At what time? (Format: YYYY-MM-DD HH:MM:SS)

downloaded file is Q4_Board_Financial_Summary.xlsx
next make sure to set the time range to the earlies of the day

Ans: 2026–08–27 08:27:03
What file stored on the Leadership site had a sensitivity label applied to it by the organization’s data governance, prior to the incident?

Ans: Q4_Board_Financial_Summary.xlsx
What file did the attacker create an external sharing link for?

Ans: Vendor_Onboarding_Notes.docx
What external email address was granted access to this file?
Ans: d.reynolds88@protonmail.com
According to the emails, what is the subject line of the notification sent to this external address by the sharing application?
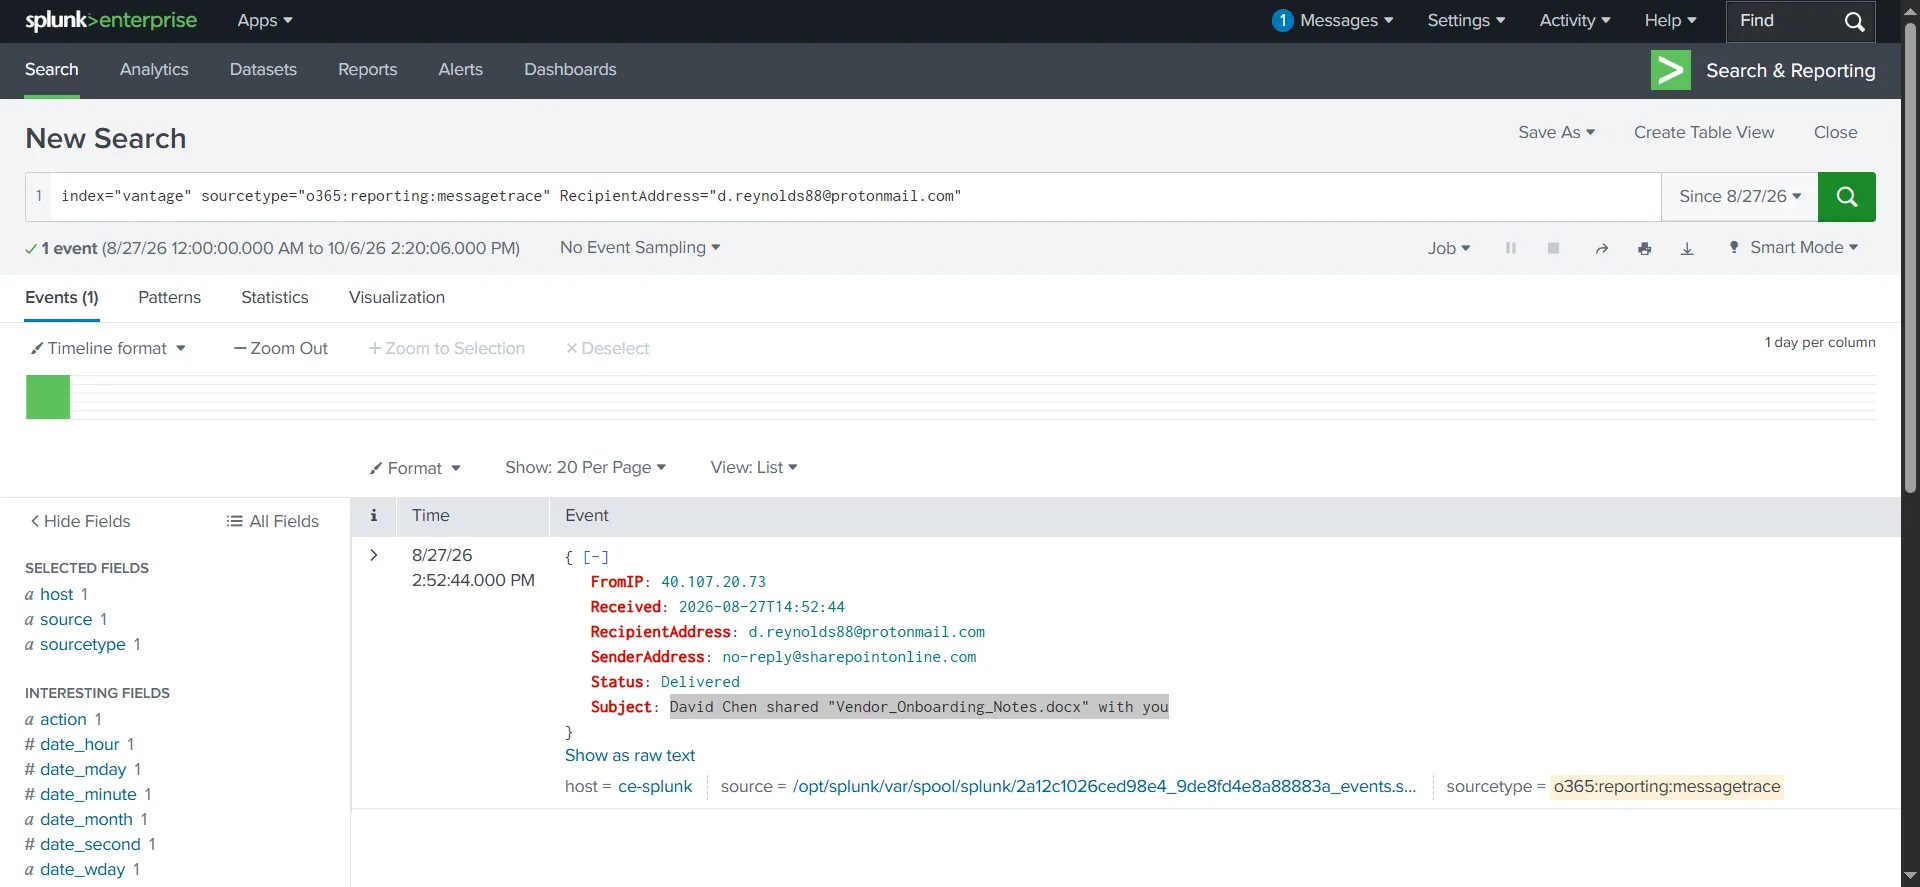
Ans: David Chen shared “Vendor_Onboarding_Notes.docx” with you
THANK YOU FOR READING!!! ❤️💫